Skip to content

Compliance checklist

Know where you stand before the auditor asks.

A working checklist of the record-keeping requirements in HIPAA, SOX, GDPR and FERPA. Mark what you have, track what is in progress and export the list for your team.
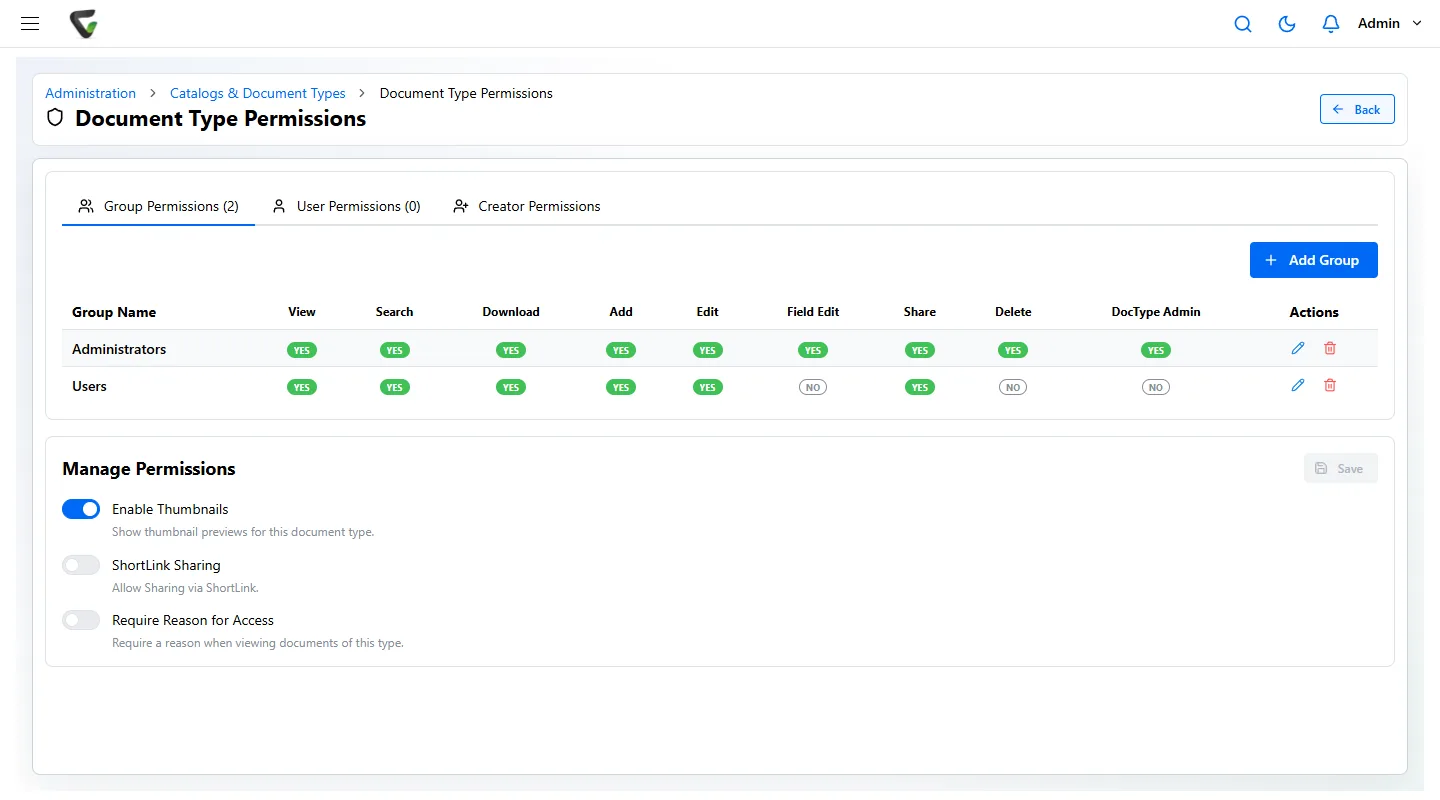
Content Central permissions by group: view, search, download, edit, share and delete

01The checklist

Pick a regulation. Work down the list.

Tap an item to move it from not started, to in progress, to done. Your answers stay on this device.

HIPAA

Health Insurance Portability and Accountability Act

Applies to

Health plans, clearinghouses and providers that bill electronically, plus their business associates

Penalties

Tiered civil penalties per violation, with annual caps in the millions, and criminal penalties for knowing misuse

  • Security risk analysis

    45 CFR 164.308(a)(1)

    Assess the risks to electronic protected health information (ePHI) and review the analysis regularly.

    AdministrativeNot started
    Evidence to keep (2)
    • Written risk analysis
    • Risk management plan
  • Named security official

    45 CFR 164.308(a)(2)

    Name one person responsible for developing and carrying out your security policies.

    AdministrativeNot started
    Evidence to keep (2)
    • Appointment record
    • Role description
  • Workforce security training

    45 CFR 164.308(a)(5)

    Give every member of your workforce security awareness training, and keep it current.

    AdministrativeNot started
    Evidence to keep (2)
    • Training materials
    • Attendance records
  • Facility and workstation security

    45 CFR 164.310

    Control physical access to the places and devices where ePHI lives, including how devices and media are disposed of.

    PhysicalNot started
    Evidence to keep (2)
    • Facility access procedures
    • Device and media disposal records
  • Access control

    45 CFR 164.312(a)

    Give every user a unique ID and limit access to ePHI to the people who need it.

    TechnicalNot startedA document system helps
    Evidence to keep (2)
    • User and group permissions
    • Access request approvals
  • Audit controls

    45 CFR 164.312(b)

    Record and review activity in the systems that hold ePHI.

    TechnicalNot startedA document system helps
    Evidence to keep (2)
    • Audit trail samples
    • Log review records
  • Integrity and transmission security

    45 CFR 164.312(c), (e)

    Protect ePHI from improper change or destruction, encrypt it where reasonable and protect it in transit.

    TechnicalNot startedA document system helps
    Evidence to keep (2)
    • Version history settings
    • Encryption settings
  • Automatic logoff

    45 CFR 164.312(a)(2)(iii)

    End sessions after a set period of inactivity.

    TechnicalNot startedA document system helps
    Evidence to keep (2)
    • Session timeout settings
    • Policy document
  • Business associate agreements

    45 CFR 164.308(b), 164.504(e)

    Sign a business associate agreement (BAA) with every vendor that creates, receives, keeps or sends PHI for you.

    AgreementsNot startedA document system helps
    Evidence to keep (2)
    • Signed BAAs
    • Vendor list
  • Keep required documentation for six years

    45 CFR 164.316(b)(2)

    Keep your policies, procedures and required records for six years from when they were created or last in effect, whichever is later.

    DocumentationNot startedA document system helps
    Evidence to keep (2)
    • Retention policy
    • Policy version history

0 done, 0 in progress, 10 not started

General guidance on common requirements, not legal advice. Rules change and your situation is your own, so confirm what applies to you with your counsel or compliance advisor.

02Where software helps

The evidence, kept as you work.

The items marked "A document system helps" are the ones Content Central takes off your plate. It helps you meet HIPAA, SOX, GDPR and FERPA, in the cloud or on your own servers.

An audit trail you never have to build

Content Central keeps an audit trail of the activity on every document, so the evidence for access and audit items builds up as people work.

Permissions by group, down to the action

Decide who can view, search, download, edit, share or delete, group by group, with Active Directory, SAML and multi-factor sign-in.

Retention and legal holds that run themselves

Set a retention period per document type, put records on legal hold when a matter opens, and keep every version along the way.

Trusted by 1,000+ organizations since 2002. Fortune 500 companies and government agencies run on Ademero, and their security, IT and legal teams review us every year. We sign HIPAA BAAs.

Free live demo

Want us to walk your checklist with you?

Book a free demo and we will show you around, answer your questions and run your real paperwork through it. No cost, no pressure.
  • A live tour of the products that fit your work
  • Your own documents, set up and shown working
  • Your workflow and process, mapped with you
  • Straight answers from people who build it
Engraved illustration: file boxes, a document scanner and a PC at a desk